Your Identity.
Your Permission.
Your Control.
AIIP is being designed around a simple principle: having an AIIP device should never mean giving everyone access to everything about you. Identity sharing should be controlled, permission-based and revocable.
Explore Our Approach
AIIP Security Starts With Architecture
Security should not be an extra feature added later. The platform is intended to separate identity, physical credentials, permissions and AI access.
User-Controlled Identity
Your AIIP Identity is designed to remain under your account rather than belonging to one physical device.
Permission First
Information should be shared according to defined permissions and consent.
Data Separation
Sensitive identity information should not simply be stored openly on an NFC ring or card.
Revocable Devices
A lost device should be removable without destroying the user's underlying AIIP Identity.
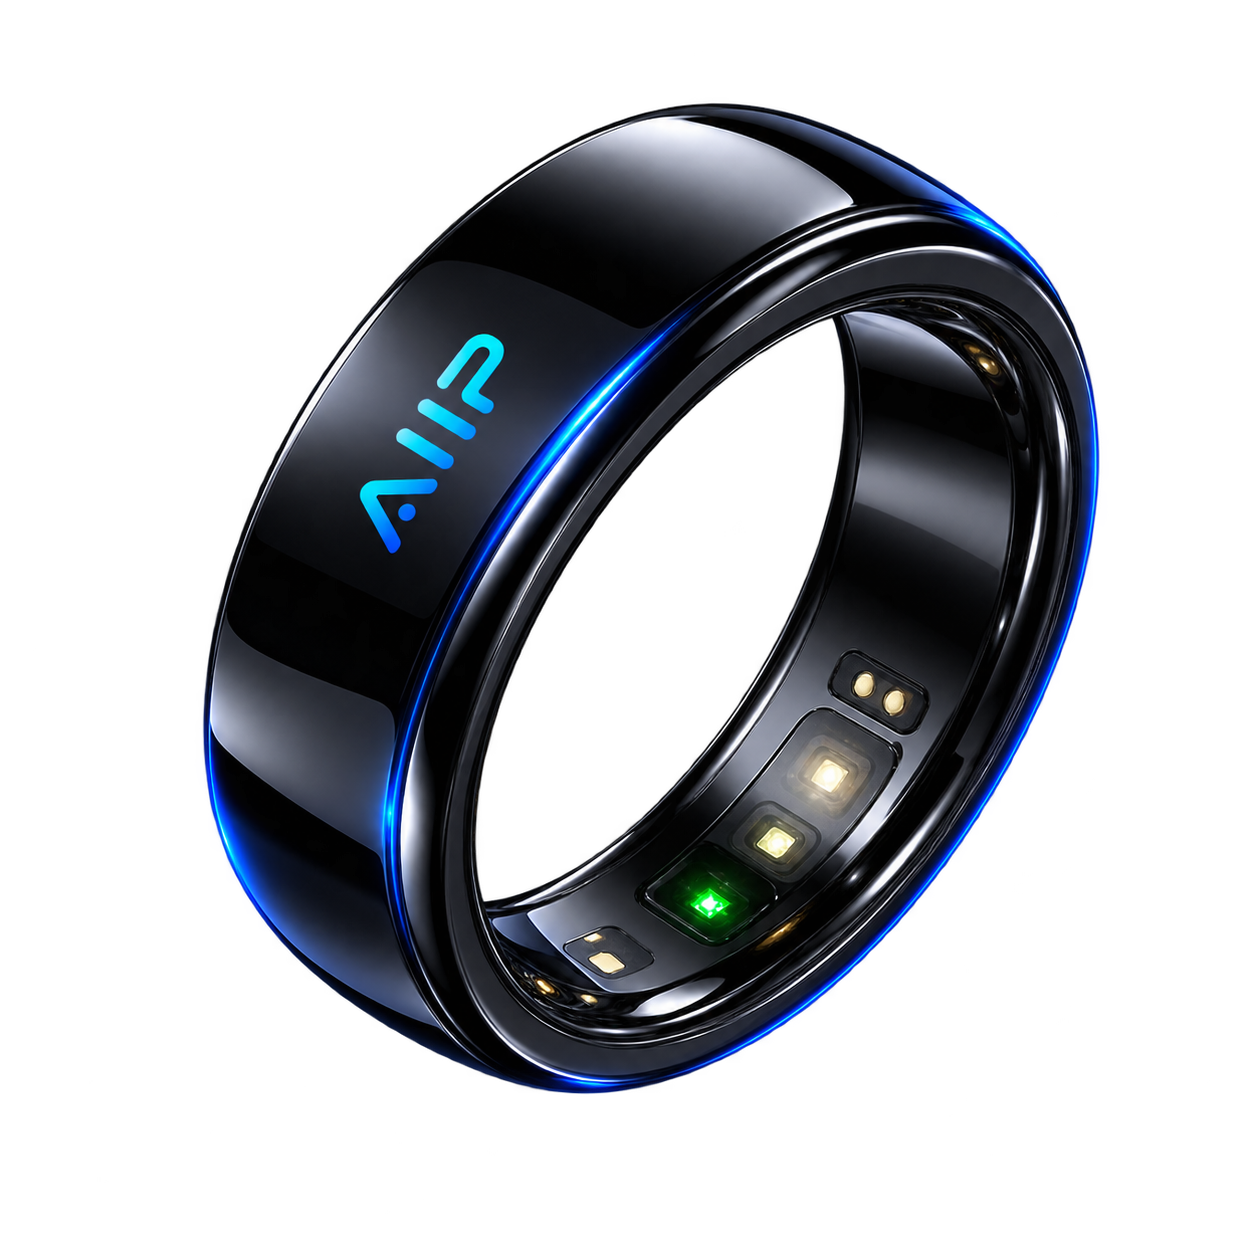
The Device Is a Key.
Not a Data Vault.
A physical AIIP device such as a Ring, Card, Bracelet or future supported device should primarily act as an identity credential or authentication interface. It should not simply expose a user's sensitive personal information to anyone who scans it.
Device Identifies the Credential
The device provides a secure way for AIIP to recognize the associated credential.
Platform Resolves the Identity
AIIP determines which identity and permissions are associated with that credential.
Permissions Decide the Result
Only the information appropriate for that interaction should be returned.
Lost Devices Can Be Revoked
Removing one credential does not require deleting the user's entire identity.
How Identity Information Should Flow
The physical device should not determine what another person is allowed to know. The AIIP permission layer does.
AIIP Device
A ring, card, bracelet or another supported credential starts the interaction.
Identity + Permission Layer
AIIP checks the associated identity, device status and sharing permissions.
Authorized Result
Only information permitted for that person, service or situation is returned.
What If You Lose Your AIIP Ring?
Losing hardware should not mean losing your entire digital identity.
Device Is Lost
The user notices that an AIIP Ring, Card or another device is missing.
Open Device Management
The user identifies the specific physical credential connected to the account.
Disable the Device
That credential can be marked inactive or revoked within the AIIP platform.
Identity Remains
The user's AIIP Identity and other authorized devices continue to exist.
AI Should Know Only What You Authorize.
AIIP's long-term vision includes helping AI assistants understand useful identity context. But AI access should not automatically mean unlimited access to a user's entire profile.
Purpose-Based Context
A business introduction may use professional information without requiring unrelated private information.
Permission-Based AI Access
Different AI services can potentially receive different levels of authorized context.
Revocable Access
Future integrations should support changing or withdrawing authorization.
Minimal Necessary Information
Systems should receive the information required for a legitimate experience, not everything available.
AIIP Security Is More Than the NFC Chip
A trusted identity platform requires multiple layers working together.
Privacy by Design
The goal is to make privacy part of the AIIP architecture rather than relying only on policy documents.
Collect Purposefully
AIIP should collect information because it serves a defined user or platform purpose, not simply because it can.
Share Minimally
An interaction should expose only the information necessary for that specific use case.
Separate Hardware From Data
The device should not become an openly readable storage location for sensitive identity information.
Give Users Visibility
Users should be able to understand which devices and permissions are associated with their identity.
Allow Revocation
Changing a user's mind should not require rebuilding their digital identity from zero.
Evolve With Regulation
Privacy, identity and AI requirements vary by country. AIIP will need to evolve with applicable legal requirements.
Security Is Part of the Build — Not a Finished Claim
AIIP is currently being developed as a platform concept and product architecture. The descriptions on this page explain the security and privacy principles AIIP is intended to follow.
As the product progresses toward production, specific technologies, authentication methods, encryption implementations, hosting architecture, compliance frameworks and independent testing will need to be finalized and documented.
Security & Privacy FAQ
Simple answers to some of the most important questions future AIIP users may ask.
Does my AIIP Ring contain all of my personal information?
That is not the intended architecture. The physical device should act primarily as a credential or identity key, while identity information and permissions are managed through the AIIP platform.
Can anyone who taps my device see everything about me?
No. AIIP is being designed so different information can have different permission levels. The result should depend on the interaction and the permissions configured by the user.
What happens if I lose my AIIP Ring?
The goal is to allow the specific lost credential to be disabled or revoked while preserving the user's AIIP account, identity and other devices.
Can different devices have different permissions?
Yes. This is a core part of the AIIP concept. For example, a networking device could use a professional profile while another device may eventually be configured for a completely different role.
Does AI automatically receive all of my information?
That is not the intended model. AI services should receive only the identity context authorized for the relevant purpose.
Is AIIP already a certified identity or security platform?
Not at this development stage. Formal security certifications, compliance frameworks and regulatory requirements will need to be addressed as the production platform develops.
Your Identity. Your Control.
Trust must be built into the identity platform from the beginning.